Ai News
Ukrainian drones hit Russian data centers: Yandex outages
Ukrainian drones hit Russian data centers, knocking Yandex, Sberbank and cloud services offline. Here’s what broke, what recovered, and what it costs.

Ukrainian drones hit Russian data centers this month, and the fallout landed on everyday apps rather than military targets alone. Three Yandex facilities — Sasovo in Ryazan region, Kaluga, and Vladimir — were struck between October 8 and October 11. The result: Yandex Go taxi bookings stalled, Yandex Pay transfers froze, Yandex Mail and Disk went dark, and even the Alisa smart-home assistant lost cloud automation. A fourth strike hit a Sberbank data center in Balakovo, Saratov region, though the bank said systems kept running.
If you run any business that depends on a single cloud region, this is the week to reread your failover plan. Because what broke in Russia was not exotic. It was the same stack — rides, payments, email, storage, ads — that most digital economies treat as background noise.
What Exactly Got Hit
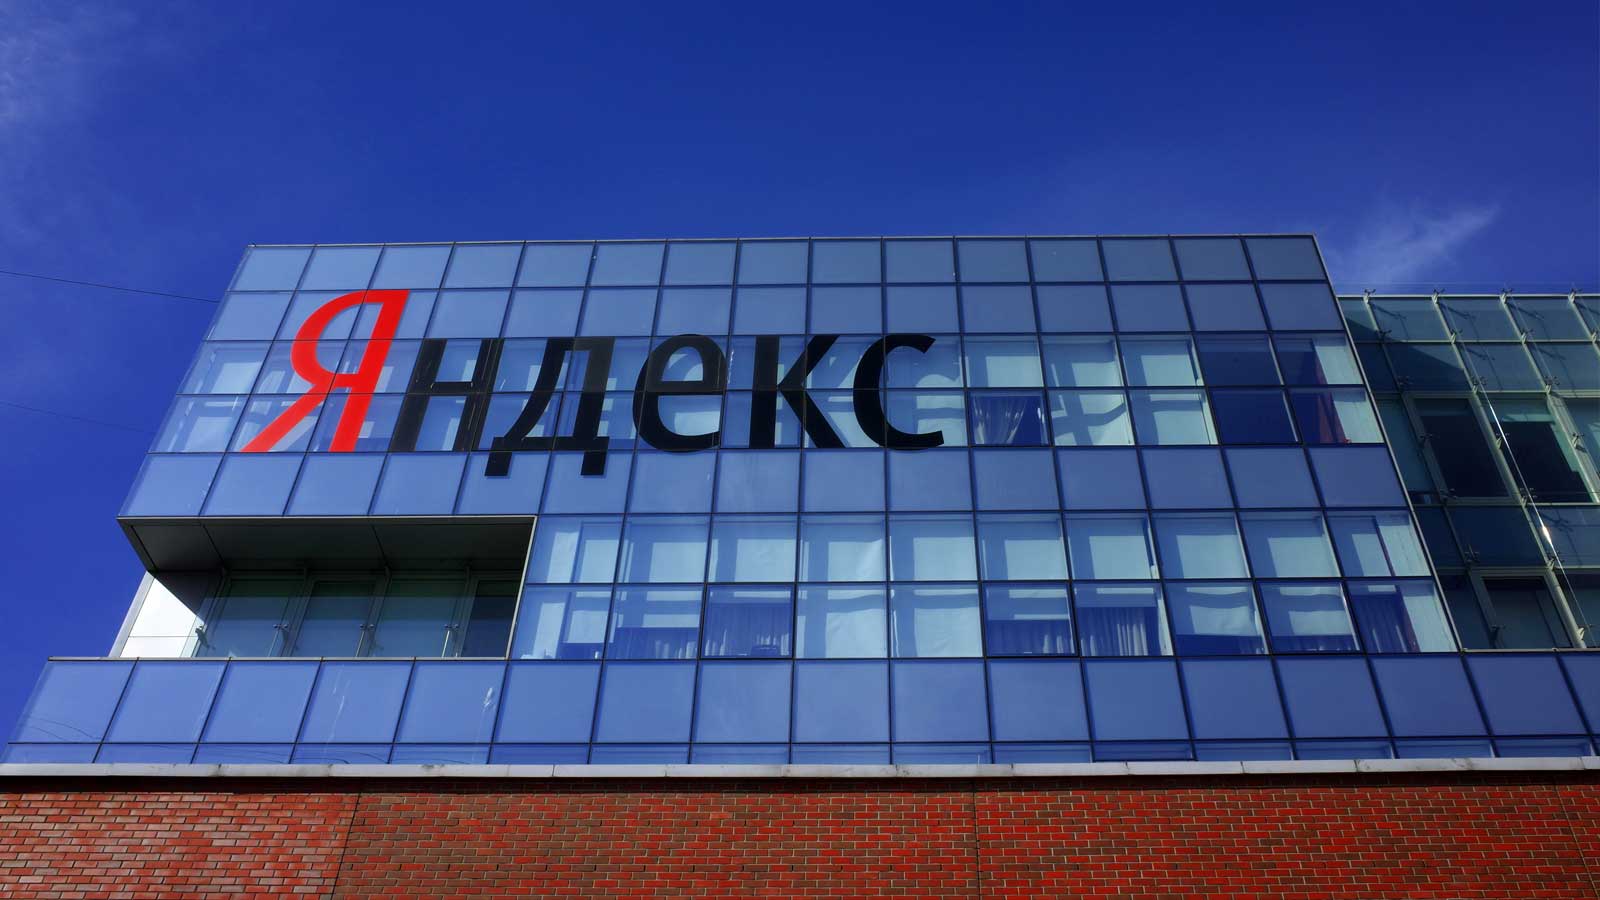
The three Yandex sites are the company’s main Russian facilities. Sasovo was severely damaged and shut down. Kaluga, described as Yandex’s largest data center in Russia, lost several modules. Vladimir was struck on October 11 and operations were “completely suspended,” according to Yandex’s own Telegram statement. The company has not given a restoration timeline, and Russian media reports suggest repairs could take months, slowed by sanctions on imported server hardware.
That matters because Yandex is not just a search engine. It runs ride-hailing, food delivery, cloud storage, mapping, advertising, and YandexGPT. Two of the company’s three supercomputers used to train that model — Chervonenkis, Lyapunov, and Galushkin — were housed at the affected sites. Yandex has not said whether the AI hardware was damaged.
How The Outage Spread To Third Parties
Yandex Cloud customers felt it first. Real estate platform Cian said its website and app resumed with limited functionality on October 12. Retailer M.Video reported disruptions on October 11. Internet provider Dom.ru also flagged service problems. Food chains Magnit and Lenta, fashion retailer Lamoda, and the Twinby dating site all reported issues, according to RFE/RL.
Yandex’s response was a mix of damage control and discounts. The company waived eligible Yandex Cloud fees from October 8 through October 31 and offered relief on personal Yandex 360 plans. It also partnered with Selectel, VK Cloud, and K2 Cloud to migrate corporate clients off its own infrastructure. Yandex Direct and Yandex Business accounts stayed restricted — advertisers could not adjust campaigns or pull reports, even though existing campaigns kept running.
The disruption crossed borders. Yandex Go holds roughly 60 percent of Moldova’s taxi market, and users there reported technical issues on October 12–13. Kazakhstan, Armenia, Belarus, and Serbia saw similar problems. Digital rights activist Sarkis Darbinian told Current Time the episode is a warning for countries that lean heavily on Yandex for taxis and maps.
Why Russia Is More Exposed Than Ukraine
Serhiy Petrenko, former head of Yandex in Ukraine, told Current Time that around 80 percent of Russia’s data centers sit in Moscow and the surrounding region. Bremen University researcher Nikolay Mitrokhin wrote on social media that 95 percent are within range of Ukrainian drones. Centralization is the vulnerability. A handful of buildings carry a disproportionate share of the country’s digital load.
Ukraine’s setup looks different. Much of its digital infrastructure runs on Amazon Web Services, which allows services to be migrated to another region — potentially another country — when a local data center is hit. Ukraine also has allies providing cybersecurity expertise and infrastructure. Russia’s allies — North Korea, Belarus, Iran — cannot offer comparable cloud capacity, and China’s walled-garden internet would be complex to integrate with Russian applications.
The Bot Traffic Claim Needs A Caveat
Early reports claimed the strikes gutted Russian disinformation bot activity. The picture is messier. Cloudflare published a report saying much of the bot traffic simply migrated to other hosts. Journalist Ilya Lozovsky posted a detailed thread explaining that bot activity did not fall off as sharply as legitimate crawlers and Yandex search functions. German tech outlet Rohtext found that online discourse declined broadly rather than targeting specific parties like the AfD.
There were real reductions in some far-right activity. But the evidence does not support the clean narrative that a drone strike switched off a troll farm. Hosting propaganda bots does not, by itself, make a data center a lawful military target under the Geneva Conventions, according to international humanitarian law expert Kubo Mačák.
What This Means For The Rest Of Us
Two lessons travel beyond the war. First, cloud concentration risk is real. Russia’s dependence on a small number of Yandex facilities turned three drone hits into nationwide app failures. If your business runs entirely in one provider’s single region, you have the same shape of exposure, just without the drones.
Second, data centers are now a wartime target class. NATO is factoring their vulnerability into planning, a senior alliance official told POLITICO. During the U.S.-Israeli conflict with Iran this year, drone strikes hit three AWS facilities in the UAE and Bahrain. The legal status of dual-use data centers remains unsettled.
For anyone evaluating cloud resilience today, the practical move is boring: multi-region backups, tested failover, and a clear list of which services can go dark for an hour without costing you customers. Yandex is offering fee waivers through October 31 because it cannot offer certainty. That is the real cost of a single point of failure.
Who Should Pay Attention
If you are a developer, CTO, or operations lead, this story is a case study. Not because you face drone strikes, but because the failure pattern — one provider, one region, one dependency chain — is common everywhere. Audit your cloud contracts this week. Ask what happens if your primary region goes offline for 30 days. If nobody can answer, you have your answer.
If you are a casual app user in Russia or a neighboring country, the near-term reality is slower payments, delayed deliveries, and unreliable taxi bookings. Yandex says it is working around the clock. Russian media says months. The gap between those two statements is where the disruption lives.
Ukrainian drones hit Russian data centers, and the blast radius reached dating apps and grocery chains. The next strike will not need to be larger. It will only need to land on another building that too many services quietly depend on.
Frequently Asked Questions
Which Yandex data centers were hit by Ukrainian drones?
Three main facilities: Sasovo in Ryazan region (October 8), Kaluga (October 9), and Vladimir (October 11). A Sberbank data center in Balakovo, Saratov region, was also targeted.
What services were disrupted by the Yandex data center strikes?
Yandex Go taxi, Yandex Pay, Yandex Mail, Yandex Disk, the Alisa smart-home assistant, Yandex Direct advertising, plus third-party services like Cian, M.Video, Dom.ru, Magnit, Lenta, Lamoda, and Twinby.
Did the strikes stop Russian bot activity online?
Not as much as early reports claimed. Cloudflare found much of the bot traffic migrated to other hosts, and journalist Ilya Lozovsky noted bot activity fell less sharply than legitimate Yandex crawlers.
Related Articles
- Big Walk Dev Explains Lack of Xbox: A Masterstroke or Missed Opportunity?
- Amazon Bee AI Devices: Frontier vs Eclipse Compared
- Billy Joel Health Update: Hydrocephalus Tests Before Tour
- Grian Chatten Solo Album: Will It Be Festival-Ready?
- Pro Dota 2 Player Claims He Had to Play a Match to Prove Identity
 Follow AFRILATEST on Google News
FIRST TIME REACTIONS:
Be the first to leave us a comment – Ukrainian drones hit Russian data centers: Yandex outages, down the comment section.
JOIN US ON OUR SOCIAL MEDIA:

Ai News
AI Agent Monitoring: What the Telemetry Bill Actually Says
AI agent monitoring now costs more than compute for 69% of enterprises running agents. What Omdia’s data shows, what it misses, and who should buy.

AI agent monitoring is the layer that watches what autonomous software does when nobody is looking, and the people selling it now have a number large enough to unsettle a finance director.
An Omdia survey of more than 300 enterprise IT decision-makers across North America and Western Europe, published through TechRadar Pro, found that 69% of organisations actively running agentic AI projects now spend more on observability than on compute and infrastructure combined. The tool built to support AI has become the single largest line item in the AI budget.
That finding is real and worth acting on. It is also a sales document, and the difference between the two matters.
What AI Agent Monitoring Actually Measures
Telemetry is the exhaust of running software: logs, metrics and traces. An agent that reasons, calls a tool, reads a document and writes an answer produces far more of it than a deterministic script, because every intermediate step becomes a signal somebody may want to retain.
The survey found more than half of respondents saw telemetry volume more than triple in the previous 12 months, averaging 3.7x, with AI and machine learning workloads accounting for roughly 43% of that growth. Looking forward, enterprises expect a 9.5x average increase from agentic workloads within two years, and nearly half are bracing for somewhere between 6x and 100x.
“This is just the beginning of the growth curve,” Omdia senior market research analyst Keir Walker said in the research. “We are at the beginning of the hockey stick.”
Using the tool is an architectural decision, not a product choice. A telemetry pipeline sits between the data sources and the expensive backend, routing, filtering, enriching and governing data before ingestion. Omdia names the three capabilities buyers want most: multi-destination routing, data reduction and sampling, and content-based routing.
Why The Telemetry Bill Now Beats The Compute Bill
Average annual observability spend sits at $3.17 million, growing 28% year over year. Thirty-five percent of enterprises report budget increases above 52%, and nearly one in five already spends more than $5 million a year on observability alone. Eighty-one percent are actively hunting for cuts.
The consequence is not only financial. Fifty-nine percent have terminated or delayed at least one agentic AI deployment because monitoring costs were too high. Among the exposure areas hit: cybersecurity monitoring, cited by 27% of respondents, and compliance and fraud detection, cited by 26%.
Read that sequence again. An organisation decides it cannot afford to watch an agent that flags fraud, so the agent is switched off. That is not a technology trade-off. It is a risk decision made by default, by whoever happens to own the observability budget.
Where The Pitch Gets Thinner
Andi Mann, who wrote the TechRadar analysis, is chief product and technology officer at Apica, a vendor that sells data pipelines. The piece runs in TechRadar Pro’s Perspectives channel, which is explicitly a platform for industry contributors. The Omdia data is the evidence; the recommendation to buy a routing layer is the author’s commercial position.
Nothing in the numbers is contradicted by that, but the framing deserves a sceptical read. The same survey shows 22% of enterprises have not begun to consider the data implications of agentic AI at all, while 35% report widespread deployment. That readiness gap suggests a lot of organisations bought agents before they bought a plan.
There is a second check the source material never makes. More agents do not automatically deliver proportionally more capability. Ramez Naam, writing via Noahpinion, argues that parallel agents scale roughly logarithmically or worse for genuine problem-solving gains, even though they work well for raw speed. OpenAI’s Navier-Stokes announcement, widely attributed to around 10,000 agents working concurrently across an 88-hour run, is the case usually cited. The agent count measures how many researchers ran, not what they contributed.
If that holds, enterprises are absorbing exponential telemetry growth to supervise agents whose output is governed by far weaker returns. The bill scales faster than the benefit.
The Data You Cannot Monitor At All
A separate problem sits outside the observability stack entirely. Research from Wake Forest University, presented at the International Conference on Automated Software Engineering in Munich in October 2026, examined third-party skills that extend large language model agents, the plugins that let an agent build a presentation from your notes or scan financial documents for compliance issues.
Ying Zhang, an assistant professor in the Department of Computer Science, and her team tested 17,022 randomly selected skills listed on SkillsMP, described as the largest open-source AI agent skill marketplace, and generated 170,226 outputs. They found credential leakage in two forms: skills that are simply flawed, and skills built to be malicious and push data back to a remote server.
No telemetry pipeline catches that one. It is a supply-chain problem, and it arrives through the same install button your team already uses.
Who Should Buy It, And Who Should Wait
Buy or build the pipeline layer if you are running agentic workloads in production, your observability bill is climbing faster than your compute bill, or you have already paused an agent over monitoring cost. The case for a filtering layer ahead of the backend is strong, and the market reflects it: 97% of respondents have implemented or are actively considering a telemetry pipeline, and 70% are in active evaluation now. Nearly one in four say existing vendor relationships are not a significant factor in the purchase decision, which means the incumbents are not safe.
Wait if your agents are still in pilot. The Omdia sample covers North America and Western Europe only, and the cost thresholds, $3.17 million average spend and $5 million for the top fifth, are calibrated to those budgets. A team in Lagos or Nairobi seeing the same 3.7x telemetry growth is not facing the same absolute figure, but it faces the same volume-based pricing model, with thinner headroom and often harder currency constraints. The number that matters there is the share of cloud spend consumed by logs, not the dollar figure quoted in the research.
Whoever you are, treat AI agent monitoring as a cost-control and risk-control purchase rather than a feature. Organisations that solved it early are, per Omdia, 50% more likely to be prepared for 6x growth and 80% more likely to have dodged the cost crunch. The rest will keep choosing between watching their agents and affording them.
Frequently Asked Questions
What is AI agent monitoring?
It is the observability layer that captures logs, metrics and traces generated by autonomous AI agents as they reason, call tools and take actions. Omdia’s research found 69% of organisations running agentic AI projects now spend more on this observability than on compute and infrastructure combined.
Why do AI agents generate so much telemetry data?
Every intermediate step an agent takes becomes a signal worth recording. More than half of surveyed enterprises saw telemetry volume more than triple in 12 months, averaging 3.7x, with AI and machine learning workloads responsible for roughly 43% of that growth. Enterprises expect a 9.5x average rise from agentic workloads within two years.
Do I need a telemetry pipeline before deploying AI agents?
If agents are in production and your observability bill is growing faster than your compute bill, yes. Omdia found enterprises with a telemetry pipeline are 50% more likely to be prepared for 6x data growth. If agents are still in pilot, the survey data is drawn only from North America and Western Europe, so the cost thresholds may not transfer to other markets.
FIRST TIME REACTIONS:
Be the first to leave us a comment – AI Agent Monitoring: What the Telemetry Bill Actually Says, down the comment section.
JOIN US ON OUR SOCIAL MEDIA:

About Xavier Catherine
Xavier Catherine is the Technology Lead at AfriLatest. With a background in computer science and a focus on innovation, he oversees the platform's technology infrastructure. Xavier also contributes reporting on AI, gadgets, and cybersecurity, ensuring AfriLatest remains secure, reliable, and user-friendly.
View all articles by Xavier CatherineAi News
Prepare For AI Agents: What They Do, Cost, And Risk
A hard look at agentic AI tools: what they actually do, what they cost, where they fail, and how to prepare for AI deployment without losing control.

The tool under review is the agentic AI platform — software that reads, writes and acts inside business systems without a human approving every step. The reasons to buy one are real. The way most organisations prepare for AI is not: purchasing is running ahead of testing, and that gap is where the damage will eventually show up.
The adoption forecast is specific. According to TechRadar Pro, Gartner expects 40% of enterprise applications to include task-specific AI agents by the end of 2026, up from less than 5% in 2025. Gartner’s advice to software leaders is to set an agentic strategy or risk being outpaced. The direction is right. The sequence is being ignored, because strategy is being signed off as procurement.
What The Tool Actually Does, And Where It Fails
An agentic system does three things a chatbot cannot. It holds credentials into real systems. It chooses sequences of actions on its own. And it calls third-party services whose security the buyer has usually not vetted. The marketing sits on top of those three facts, and so do the risks.
The failure record already exists. TechRadar Pro cites the Hugging Face breach, which was traced to a rogue AI agent. Prompt injections arrive looking harmless and turn hostile later, sometimes long after the integration shipped. Deepfake tooling can spin up a malicious bot for around $1,000 — less than the cost of cleaning up after one incident.
Shadow AI compounds all of it. Employees adopt unsanctioned tools to finish routine tasks and reporting, which means the data map is often wrong before the agent even arrives. Security teams end up auditing a system of record that no longer reflects what people actually use.
That is not a case against agents. It is a case against deploying them before you know which of those three facts you control. On the evidence in the source material, most teams do not: access is being granted to agents across sensitive data, frequently bypassing standard enterprise controls.
How To Prepare For AI Deployment Without Handing Over The Keys
The workable sequence starts with identity, not with the model. Know who or what is acting on the data. Authorise contextually rather than implicitly. Validate behaviour and intent continuously. Keep a named human accountable at every stage. “The machine did it” does not survive a board review.
The same discipline appears in professional training. Bloomberg Law reports Cleary Gottlieb partners arguing that AI fluency is not “good prompting”. It is knowing where to use AI, defining the task, identifying relevant sources, testing output and validating results. A junior lawyer reviewing an AI draft needs enough grounding to spot weak reasoning. The argument generalises well beyond law: whoever signs off on the output must be able to tell a good answer from a fluent one.
Measurement matters as much as governance. At SEMICON Taiwan 2026, Microsoft’s Rani Borkar pushed what the company calls the “yield imperative” — judging AI infrastructure by useful output per dollar and per watt rather than by capacity built, as detailed in Microsoft’s account of the keynote. It is a supplier’s framing, and it is still the right question for a buyer: what does this system demonstrably produce, and at what cost?
Where The Bills And The Breaches Come From
The cost asymmetry is the strongest argument in the source material. The estimated annual cost of cybercrime is $10.5 trillion globally, predicted to reach $15.63 trillion by 2029. Gartner’s forecast for information security spending in 2026 is $244 billion. One number is roughly forty times the other. No enterprise budget will close that gap alone.
There is a second cost line for teams outside the biggest markets. AI contracts, cloud capacity and security tooling are priced in dollars while revenue is local. For a mid-sized firm in Lagos, Nairobi or Accra, a serious incident is not only a technical event. It is a currency event, because the remediation bill arrives in hard currency and the lost revenue does not. That is the practical meaning of the imperative to prepare for AI: not a strategy document, but a tested list of what an agent can reach inside your business.
Alternatives Worth Considering First
Three options sit below full autonomy. Read-only assistants that draft and summarise but cannot write to production systems. Human-approval gates on any action touching money, personal data or external parties. And delay — spending the next two quarters on identity, logging and a rehearsed incident response before any agent receives credentials. None of these is exciting. All three are cheaper than a breach.
There is also the encryption clock. Security leaders are counting down to “Q-Day”, when quantum computers become powerful enough to break the encryption standards in wide use today. Any agent holding long-lived credentials adds to that exposure.
The trust argument supports the slow route. PwC’s 25th Annual Global CEO Survey, cited in the TechRadar Pro piece, found that customer trust explained 31% of the variance in profit margins and 21% in return on assets — a stronger link to financial performance than company size.
Who Should Prepare For AI Now, And Who Should Wait
Organisations with a named data owner, an audited inventory of where sensitive data lives, and an incident log they are willing to test should move. They can absorb an agent failure, investigate it and report it. Organisations that cannot yet say which systems hold customer records should not hand credentials to software that decides for itself.
They should prepare for AI by fixing that list first, because an agent with access to data you cannot map is a breach with a schedule.
The tool is not the problem. Buying it to skip the preparation is.
Frequently Asked Questions
What does an agentic AI tool do that a normal AI assistant does not?
It holds credentials into real business systems, decides on sequences of actions by itself, and calls external services. That combination is what expands the attack surface, because the agent can move data and trigger workflows without a person approving each step.
How much does AI-related cybercrime actually cost compared with security spending?
The source material puts the annual global cost of cybercrime at $10.5 trillion, rising to a predicted $15.63 trillion by 2029, against Gartner’s forecast of $244 billion in information security spending for 2026. The gap is roughly forty to one, which is why individual budgets cannot buy their way out of the risk.
What is the minimum safe starting point before giving an AI agent access to company data?
Three things: a named human accountable for the agent’s actions, an identity and permission model that authorises contextually rather than implicitly, and continuous validation of behaviour and intent. If the organisation cannot yet map where sensitive data lives, that inventory comes first.
Are there cheaper alternatives to deploying fully autonomous AI agents?
Yes. Read-only assistants that draft and summarise without writing to production systems, human-approval gates on any action touching money or personal data, and a deliberate delay while identity, logging and incident response are tested.
FIRST TIME REACTIONS:
Be the first to leave us a comment – Prepare For AI Agents: What They Do, Cost, And Risk, down the comment section.
JOIN US ON OUR SOCIAL MEDIA:
About Xavier Catherine
Xavier Catherine is the Technology Lead at AfriLatest. With a background in computer science and a focus on innovation, he oversees the platform's technology infrastructure. Xavier also contributes reporting on AI, gadgets, and cybersecurity, ensuring AfriLatest remains secure, reliable, and user-friendly.
View all articles by Xavier CatherineAi News
AI Scam Protection in 2026: What Actually Works
A practical buying guide to AI scam protection in 2026: free phone defences, $6 to $50 monitoring tiers, and what these tools genuinely cannot do.
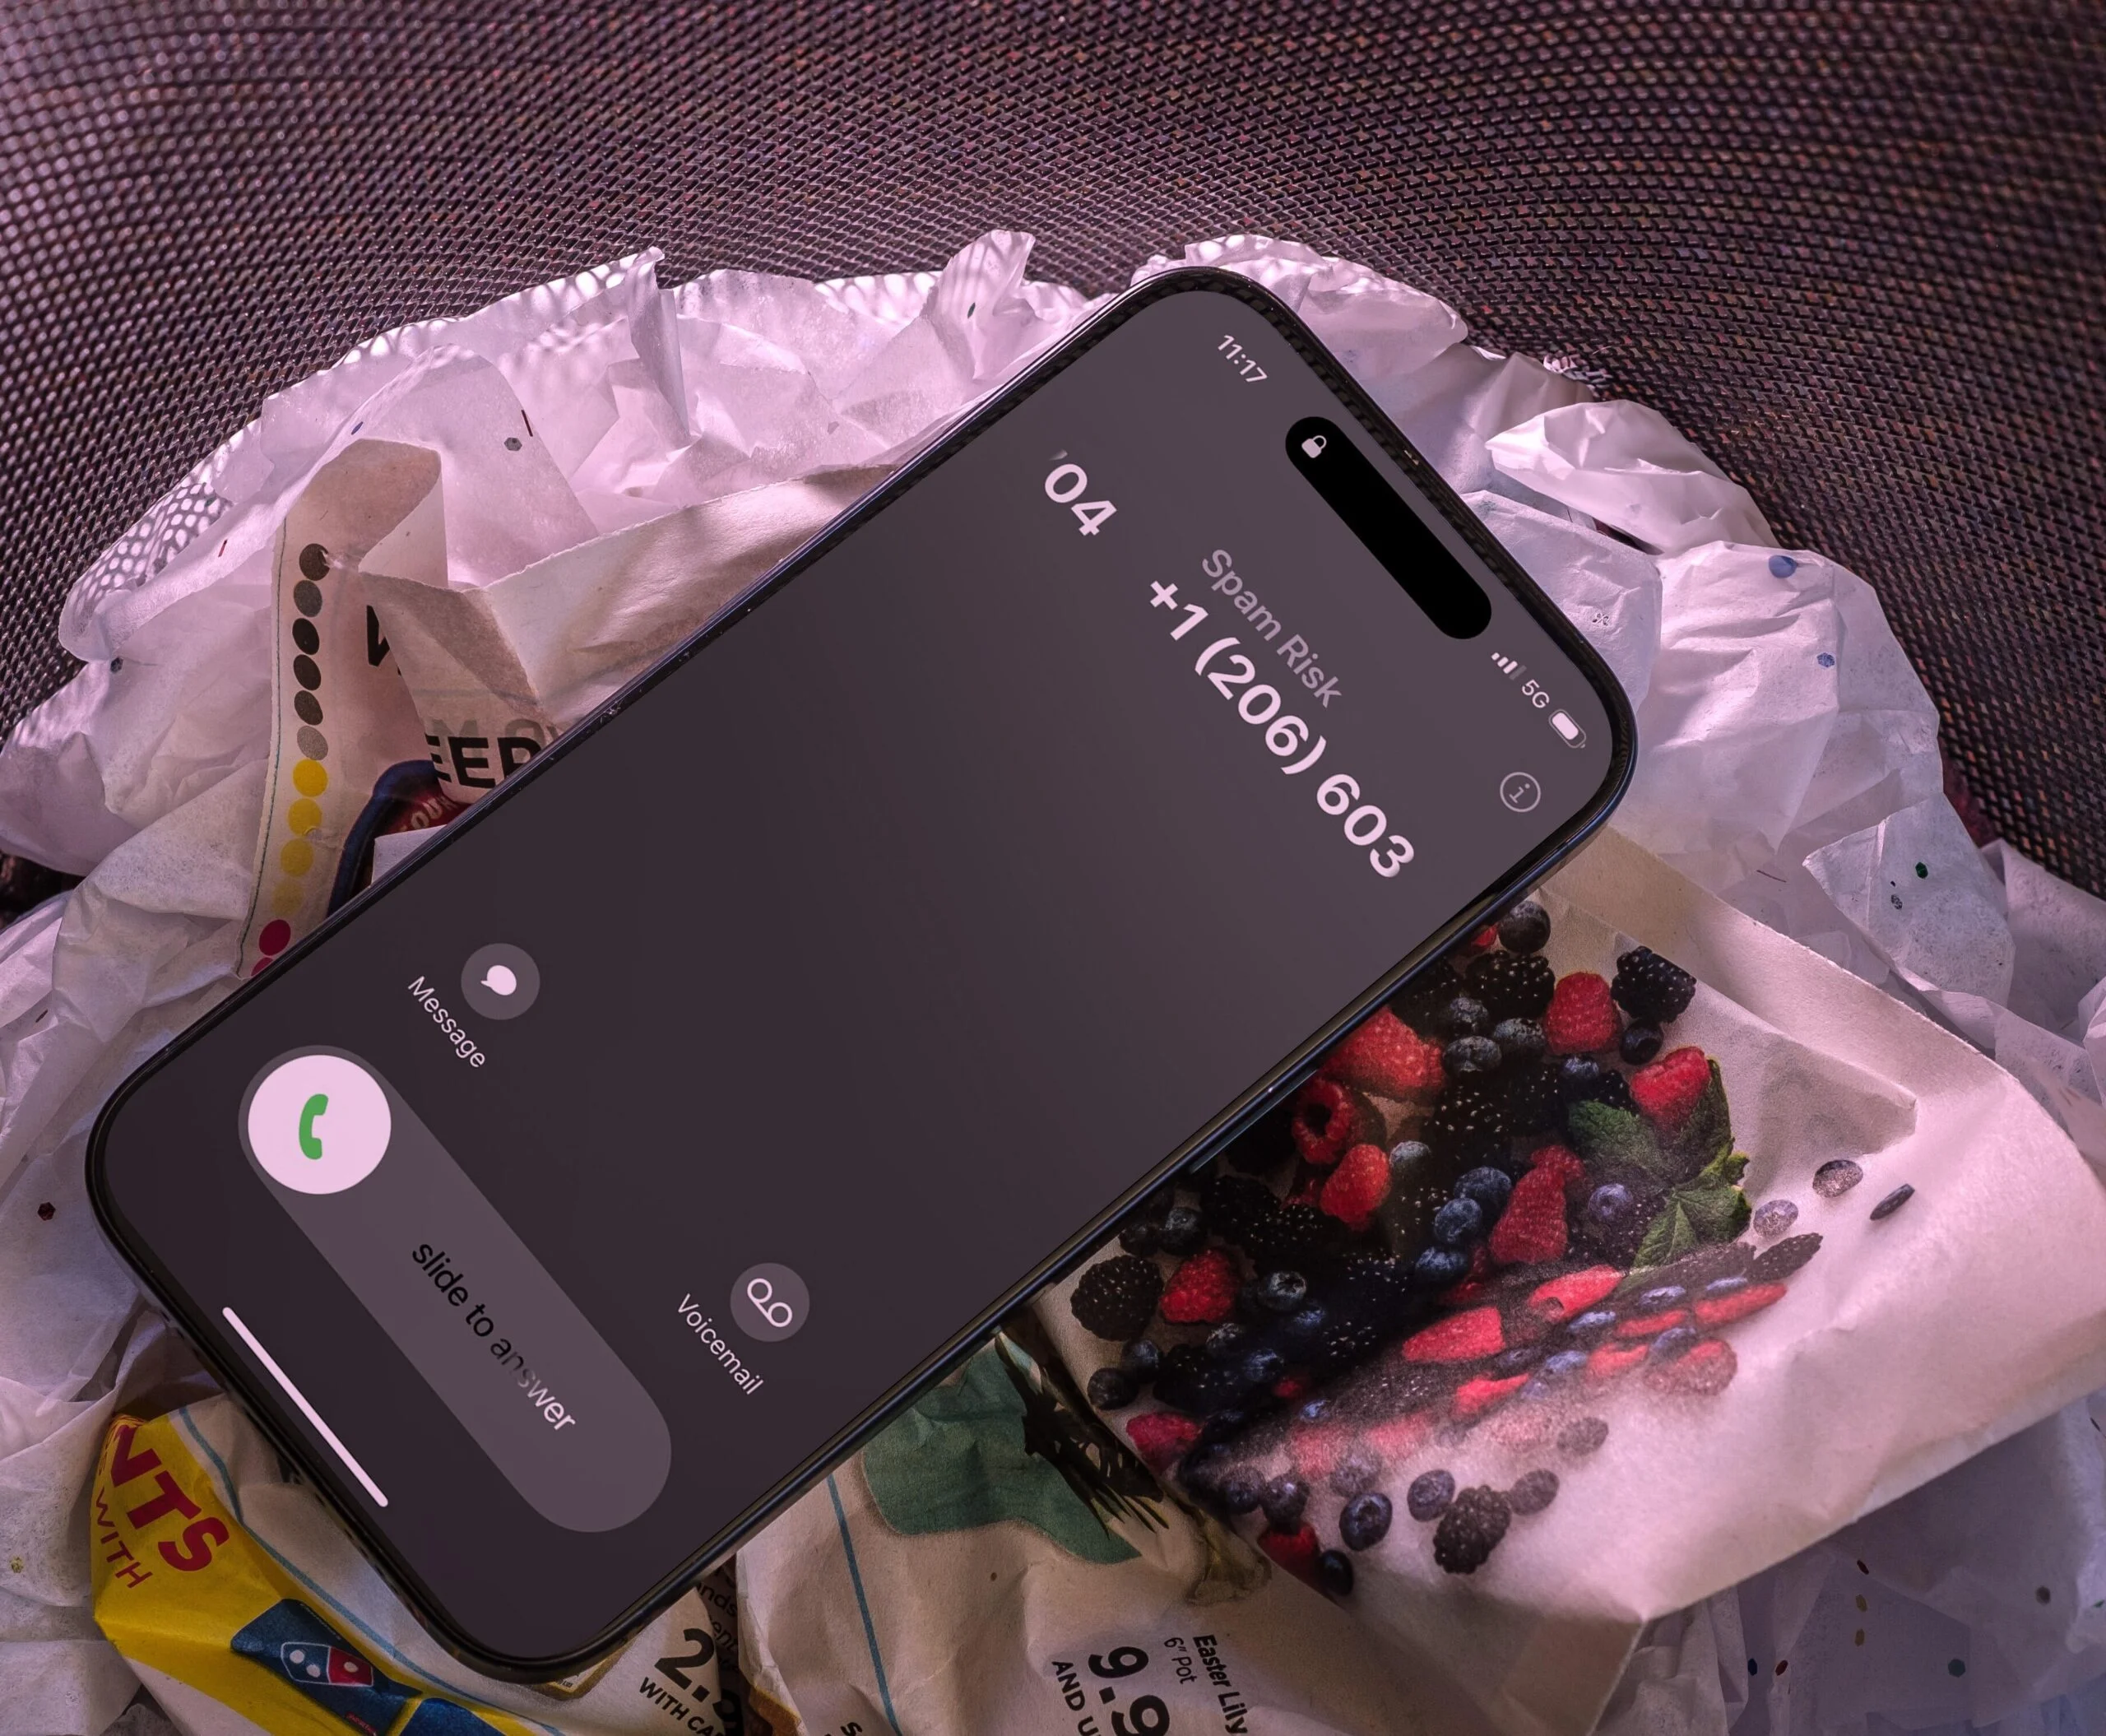
The buying question facing households in 2026 is not whether AI scams are real. It is what, if anything, is worth paying to stop them. Search for AI scam protection and you meet a crowded shelf of subscriptions promising alerts, insurance and recovery specialists. Almost none of them will stop the call that empties an account. That gap between what is sold and what is delivered is the only thing worth reviewing.
The scale is documented, not anecdotal. Voice security firm Hiya’s State of the Call 2026 report found that US consumers received an average of 10 spam calls per week, and that 1 in 12 people surveyed lost money to a phone scam in 2025, at an average of $682 per loss. The FBI’s Internet Crime Complaint Center logged more than one million reports and over $20 billion in losses that year, according to KUOW. Numbers like these explain why the protection market exists. They are also why it deserves scrutiny.
What The Record Shows AI Scam Protection Can Do
Call authentication was meant to solve this. In 2021 the FCC mandated Stir/Shaken, requiring major US voice providers to verify where calls originate so that Caller ID means something. Margot Saunders, senior counsel at the National Consumer Law Center, told CNET the system is not working as intended, because providers can rent thousands of numbers to telemarketers and scammers who technically comply without revealing accurate caller ID. She said the volume of unwanted calls is about the same as it has been for years. A December 2023 FCC rule only took effect in early 2025, and she expects litigation, not technology, to move the number.
On the handset, the free layer has quietly improved. iOS 26 includes call screening that intercepts unknown callers before the phone rings. Behaviour still does most of the work: do not answer, do not press a button to be removed from a list, do not say yes, and never trust a caller claiming to be a bank or a government agency. Hang up and dial a published number.
Detection has also become easier in one narrow way. When KUOW reporter Katie Campbell was impersonated, at least 43 authors received long, sycophantic, clearly AI-generated emails offering book club interviews and then requesting payment for them. At least one person paid. The giveaways were formatting and overblown praise, which is a free detection method any household can learn. Anthropic’s September 2026 threat intelligence report supplies the attacker’s side of the same story: AI has collapsed the labour gap, so a lone operator with stolen API keys can now sustain multi-victim campaigns that a year earlier required skilled teams. Sophistication has stopped being a reliable signal of who is behind an operation, the company wrote in its report.
Three Budget Tiers For AI Scam Protection
Free, and this is where scams are actually stopped. The zero-cost package is phone settings plus a rule: treat every unrecognised number as hostile until verified out of band. It costs nothing, blocks the confirmation signal scammers sell to each other, and works on any handset in any country.
Under $15 a month. Coveron’s Scam Protection plan starts at $5.99 per month billed annually, with up to $2 million in identity theft restoration coverage and a 30-day money-back guarantee. It limits three-bureau credit monitoring to its Platinum tier, is unavailable in Washington and New York, and renews at significantly higher prices. Aura’s Kids plan is $13 monthly, or $10 billed annually, per Money.com’s comparison.
$15 to $50 a month. Aura was rated the strongest all-round service in that review of 25 providers against 28 data points. Individual plans cost $15 monthly or $12 annually, couples $29 or $22, families $50 or $32. The family tier carries up to $5 million in insurance, three-bureau monitoring appears on every tier rather than only the top one, and annual plans have a 60-day money-back window. It bundles a VPN, antivirus and an ad blocker. Its listed weaknesses are real: no antivirus on iOS, social media monitoring for children only, and no cheap entry tier. LifeLock was named best for families, though current pricing was not confirmed in the source material.
The honest caveat comes from the same review. These services cannot prevent criminals from stealing information, will not cover all funds taken from a bank account, and exclude pre-existing fraud and non-monetary harm. They are detection and recovery products. Prevention happens in the first ten seconds of a call, and that part is free.
The Gap African Households Should Notice
Every plan above is built around US plumbing: Social Security numbers, three-bureau credit files, US insurer underwriting. A family in Lagos or Nairobi paying $50 a month for a family tier may be buying monitoring that has nothing local to monitor. Whether Aura, LifeLock or Coveron ingest Nigerian BVN or Kenyan identity data was not confirmed in the source material, and none of the vendor material reviewed addresses it.
The structural difference matters more than the price. Nigeria’s defences lean on SIM registration and identity linkage rather than call-origin authentication of the Stir/Shaken kind. The dominant loss channel is the mobile wallet, not the credit card, and wallet fraud is resolved through the bank or telco, not through a US credit bureau. Meanwhile the scam that reached KUOW’s authors was not geographically bounded: most targets were outside Washington state and some outside the US entirely. A Nigerian author, small publisher or freelance publicist is precisely the target Anthropic describes, because the marginal cost of emailing 43 people instead of one is close to zero.
Verdict
The top pick is the free layer, applied strictly: screen unknown calls, never confirm your number by answering, and verify any money request by dialling a number you looked up yourself. It outperforms every subscription because it acts before the fraud rather than after it. The runner-up for US-based households is Aura’s family plan at $32 a month billed annually, the only tier reviewed here that pairs broad monitoring with usable insurance; Coveron is the budget alternative if three-bureau monitoring is not required. For African families, the strongest AI scam protection available today is still free, and the paid market has not caught up.
Don’t Leave the “First Ten Seconds” to Chance
The article above makes one thing clear: no $50-a-month subscription will save you if you pick up the phone and start talking to a scammer. The only real defense is a rehearsed, family-wide protocol that stops the conversation before the money moves.
The 2026 Scam Survival Handbook (Large Print Edition) is the physical checklist you need for those first ten seconds. It provides the exact scripts to use when a scammer calls, the safe-word system to set up with your family, and the step-by-step verification rules for mobile wallets and bank transfers.
-
Price: $14.99 (Paperback) / $9.99 (Kindle)
-
Where to buy: [Get your copy on Amazon here|AMAZON BOOK_DIRECT LINK]
Frequently Asked Questions
Do identity theft protection services stop AI scam calls?
No. The review of 25 services states plainly that they cannot prevent criminals from stealing information, will not cover all funds taken from a bank account, and exclude pre-existing fraud and non-monetary harm. They detect exposure and help with recovery after a loss.
What is the single most effective free defence against AI voice scams?
Do not answer unrecognised numbers, and never confirm your number is active by replying, pressing a button or saying yes. Answering marks the line as live and can get it resold. Verify any request for money by calling back on a publicly listed number.
Will Aura or LifeLock monitor Nigerian or Kenyan identity data?
That was not confirmed in the source material. Their advertised features centre on US Social Security numbers and three-bureau US credit files, so families outside the US should confirm local coverage in writing before paying for a family tier.
Receive alerts for AI scam protection and more like it.
FIRST TIME REACTIONS:
Be the first to leave us a comment – AI Scam Protection in 2026: What Actually Works, down the comment section.
JOIN US ON OUR SOCIAL MEDIA:
About Xavier Catherine
Xavier Catherine is the Technology Lead at AfriLatest. With a background in computer science and a focus on innovation, he oversees the platform's technology infrastructure. Xavier also contributes reporting on AI, gadgets, and cybersecurity, ensuring AfriLatest remains secure, reliable, and user-friendly.
View all articles by Xavier Catherine-

 Startups1 month ago
What a Successful Dangote Refinery IPO Really Says
-
Savings & Investing1 week ago
Hidden Medicare Fees Draining Your Retirement Savings
-
Health and Fitness3 weeks ago
Curly Hair Hydration: 5 Proven Steps That Actually Work
-
Tech & Gadgets4 weeks ago
Apple Watch and AirPods Fall Deals: Save $120 Today
-
University Admissions1 month ago
UNILAG 2026/2027 Admission: Direct Entry & Post-UTME Guide
-
Football1 month ago
South Carolina vs Alabama: Tide Roll to 35-10 Halftime Lead
-
Trending Entertainment News4 weeks ago
Taylor Swift Joins Beatles as Only Acts With 100 Weeks at No. 1
-
Football1 month ago
Mexico vs Colombia 2026: Márquez Debut Ends in Defeat